This article introduces OpenTelemetry Go Compile-Time Instrumentation v1, enabling zero-code, build-time observability for Go applications.
This article introduces KubeSkoop, an eBPF-based ACK tool offering zero-instrumentation, pod-level Kubernetes network visibility for diagnosing DNS timeouts and TCP resets.
This article introduces OBI, a zero-code, kernel-level solution that automatically captures full AI agent invocation chains and emits GenAI-compliant OpenTelemetry traces and metrics.
This article introduces how CloudMonitor 2.0 leverages OpenTelemetry eBPF Instrumentation (OBI) to achieve full-stack observability with zero code changes.
Alibaba Cloud and Datadog jointly released an open-source OpenTelemetry Go tool enabling zero-code tracing via compile-time injection.
This article focuses on introducing and comparing several official observability solutions recommended for the Gin framework.
This article focuses on introducing and comparing several official observability solutions recommended for the Gin framework.
The article explains how to detect, reproduce, and mitigate MCP “tool poisoning” attacks by combining eBPF-based observability with large-model security evaluation.
This article describes why the Alibaba Cloud Compiler Team and Observability Team chose compile-time instrumentation to monitor Go applications.
This article introduces the importance of monitoring microservices in modern software architecture, and highlights the eBPF edition of application monitoring.
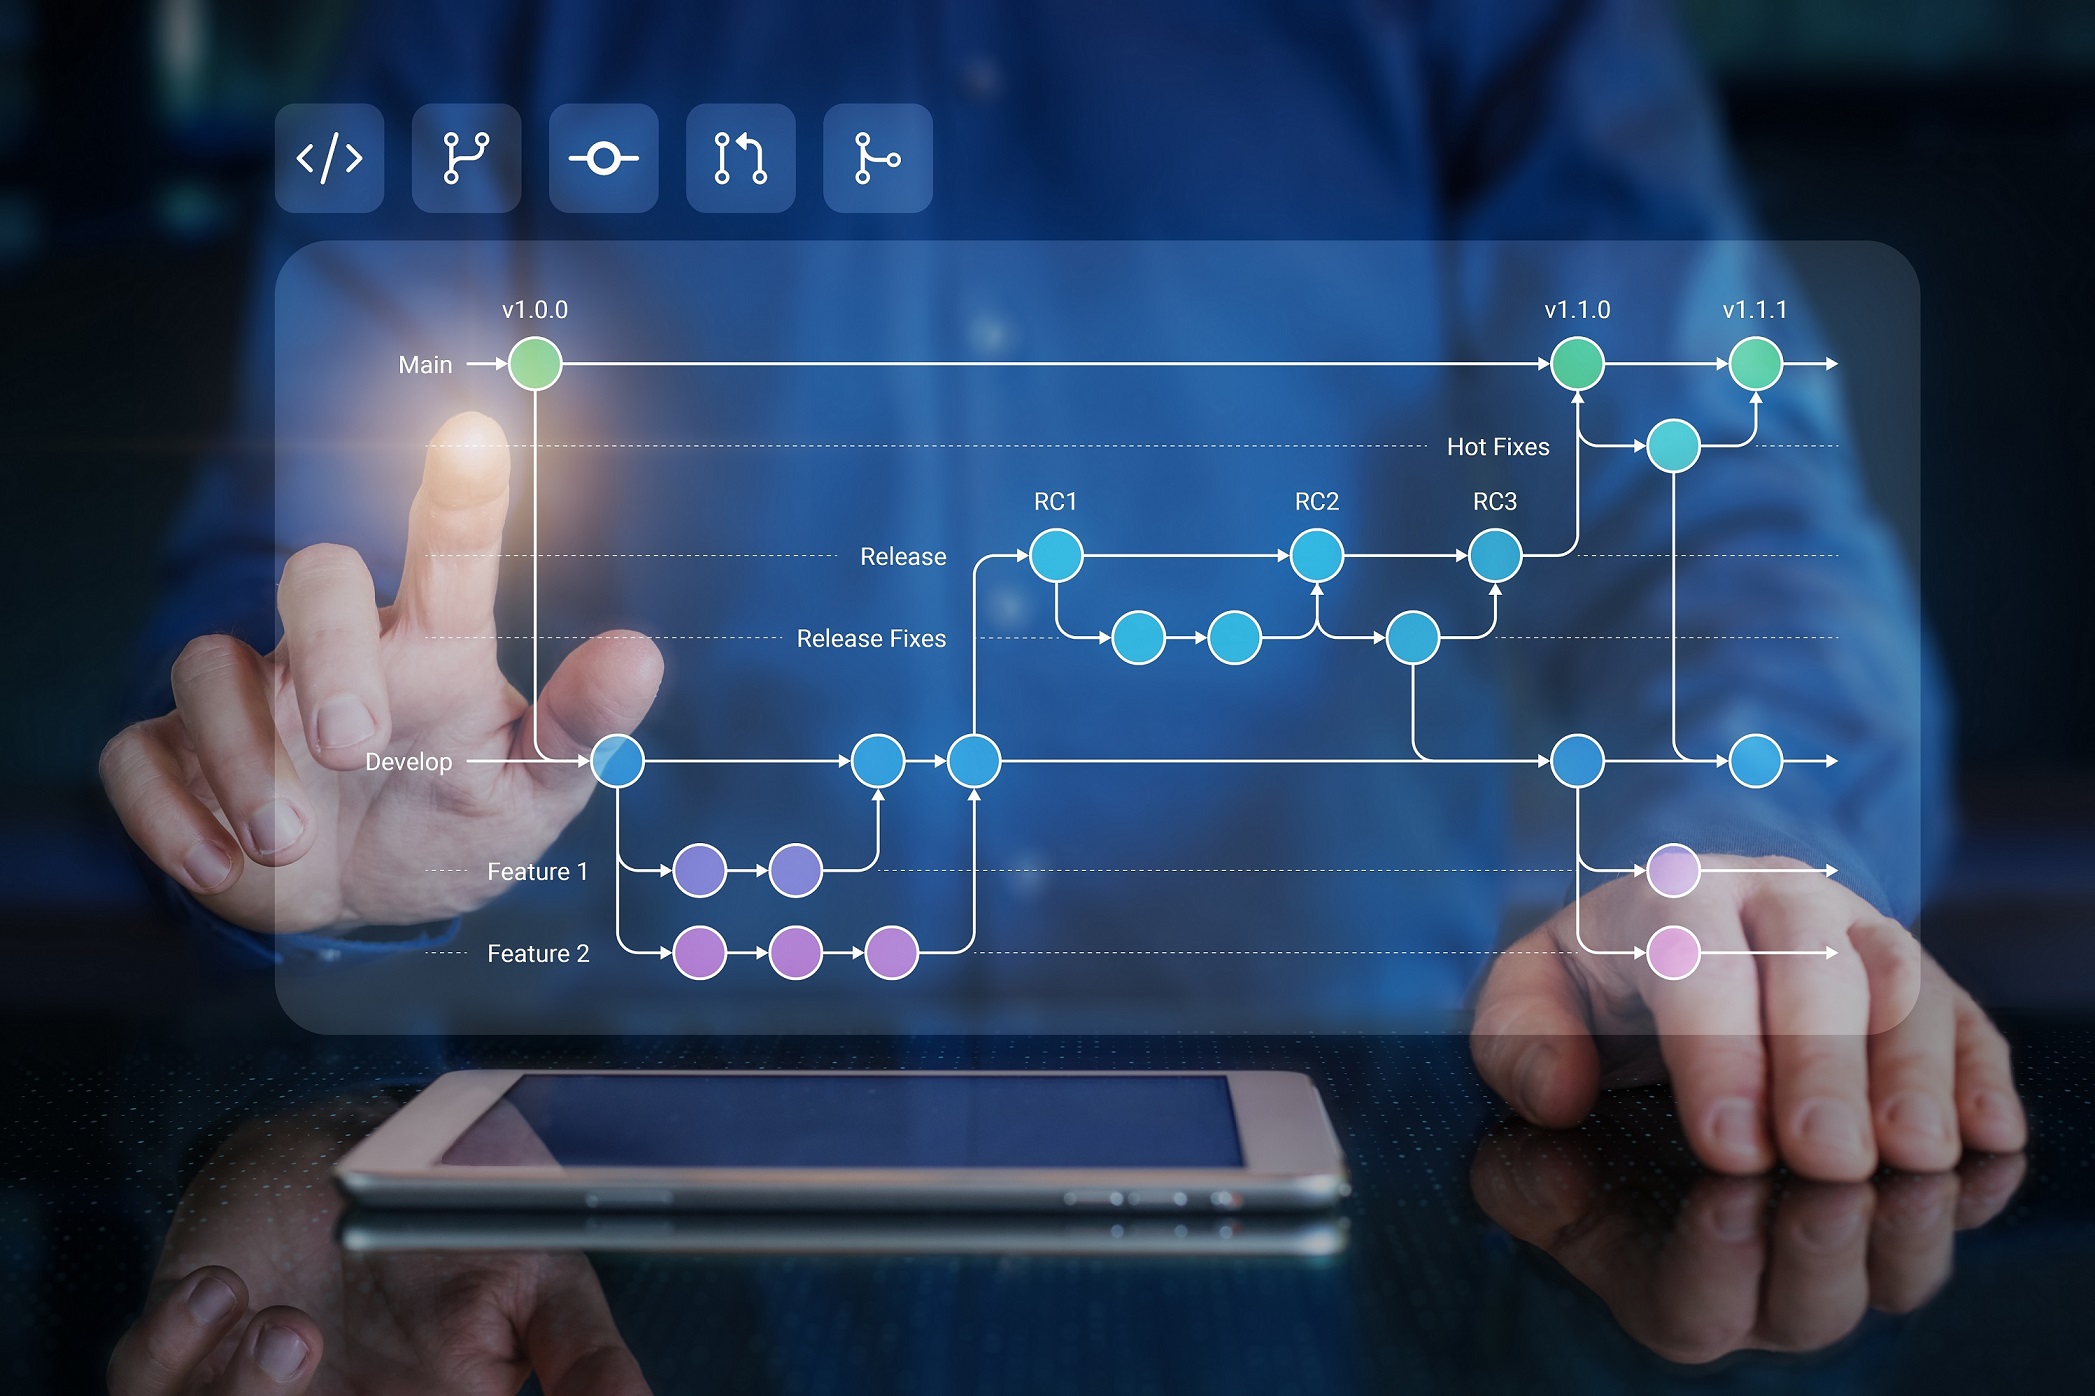
This article explores an efficient protocol parsing solution within the eBPF edition for effective observability in cloud-based microservice software architectures.
This article introduces three major observability challenges in the Kubernetes environment, and explained the solution of data collection in the Kubernetes environment.

This article introduces how the ARMS application monitoring eBPF edition meets the growing need for observability.
This article describes how to enable cgroup v2 on Alibaba Cloud Container Service for Kubernetes.
This article introduces Extended Berkeley Packet Filter (eBPF) technology and explains its advantages and disadvantages.
This article is an excerpt from a speech about Coolbpf Application Practice from the 2022 Apsara Conference.

This article is an excerpt from a speech about eunomia-bpf from the 2022 Apsara Conference.

This article introduces the eBPF technology by answering seven core questions.
This article highlights a speech from the PODS 2022 Conference, discussing the author’s insights on kernel security.
How can we use socket eBPF to improve the performance of the Kubernetes Service?


